Compare versions
Version 1 → Version 2 (current). Removed · Added. This shows the entry's text as it is written, including its formatting marks.
Version 1 · Version 2 (current) · Version history
Side by side · Together
Version 1Version 2 (current)
The Lazarus Group is the name used by cybersecurity researchers and several governments for a hacking group that the United States and the United Kingdom say works for the government of North Korea, blamed for the 2014 Sony Pictures attack, the 2017 WannaCry ransomware outbreak and large thefts of cryptocurrency.
The Lazarus Group is a hacking group that the United States and the United Kingdom say works for the government of North Korea. It is blamed for the 2014 Sony Pictures attack, the 2017 WannaCry ransomware outbreak and large thefts of cryptocurrency.
27 unchanged paragraphs
## The name and its uses
## The name and its uses
The name comes from private security research. In February 2016 a group of security companies, among them Novetta, Kaspersky Lab, AlienVault and Symantec, published reports on the actor behind the 2014 attack on Sony Pictures Entertainment, which they [dubbed "the Lazarus Group"](https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/). The researchers wrote that it had been [active since at least 2009, and possibly as early as 2007](https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/), and tied it to more than 45 families of malicious software (malware) and to earlier campaigns known as Dark Seoul and Operation Troy. Those reports [did not directly accuse North Korea](https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/), although, as SecurityWeek reported at the time, the evidence they presented suggested it could be responsible.
The name comes from private security research. In February 2016 a group of security companies, among them Novetta, Kaspersky Lab, AlienVault and Symantec, published reports on the actor behind the 2014 attack on Sony Pictures Entertainment, which they [dubbed "the Lazarus Group"](https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/). The researchers wrote that it had been [active since at least 2009, and possibly as early as 2007](https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/), and tied it to more than 45 families of malicious software (malware) and to earlier campaigns known as Dark Seoul and Operation Troy. Those reports [did not directly accuse North Korea](https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/), although, as SecurityWeek reported at the time, the evidence they presented suggested it could be responsible.
The label does not describe a single fixed team, and different organizations divide the activity in different ways. The U.S. Treasury treats "Lazarus Group", "Bluenoroff" and "Andariel" as three groups, describing them as names [commonly used "within the global cyber security private industry"](https://home.treasury.gov/news/press-releases/sm774). A 2022 U.S. government advisory notes that the actor it was describing is [commonly tracked by the cybersecurity industry as "Lazarus Group, APT38, BlueNoroff, and Stardust Chollima"](https://www.cisa.gov/news-events/cybersecurity-advisories/aa22-108a), while the FBI uses its own name, TraderTraitor, for one strand of North Korean activity aimed at cryptocurrency companies ([FBI, 26 February 2025](https://www.ic3.gov/PSA/2025/PSA250226)).
The label does not describe a single fixed team, and different organizations divide the activity in different ways. The U.S. Treasury treats "Lazarus Group", "Bluenoroff" and "Andariel" as three groups, describing them as names [commonly used "within the global cyber security private industry"](https://home.treasury.gov/news/press-releases/sm774). A 2022 U.S. government advisory notes that the actor it was describing is [commonly tracked by the cybersecurity industry as "Lazarus Group, APT38, BlueNoroff, and Stardust Chollima"](https://www.cisa.gov/news-events/cybersecurity-advisories/aa22-108a), while the FBI uses its own name, TraderTraitor, for one strand of North Korean activity aimed at cryptocurrency companies ([FBI, 26 February 2025](https://www.ic3.gov/PSA/2025/PSA250226)).
## Attribution to North Korea
## Attribution to North Korea
On 13 September 2019 the U.S. Treasury's Office of Foreign Assets Control imposed sanctions on the Lazarus Group, Bluenoroff and Andariel, identifying them as agencies or controlled entities of the government of North Korea ([U.S. Treasury, 13 September 2019](https://home.treasury.gov/news/press-releases/sm774)). The Treasury states that all three are controlled by the Reconnaissance General Bureau (RGB), which it calls North Korea's primary intelligence bureau and which was already under U.S. and United Nations sanctions. It describes the Lazarus Group as created by the North Korean government "as early as 2007" and subordinate to the RGB's 110th Research Center, 3rd Bureau, and lists its targets as government, military, financial, manufacturing, publishing, media, entertainment and international shipping companies.
On 13 September 2019 the U.S. Treasury's Office of Foreign Assets Control imposed sanctions on the Lazarus Group, Bluenoroff and Andariel, identifying them as agencies or controlled entities of the government of North Korea ([U.S. Treasury, 13 September 2019](https://home.treasury.gov/news/press-releases/sm774)). The Treasury states that all three are controlled by the Reconnaissance General Bureau (RGB), which it calls North Korea's primary intelligence bureau and which was already under U.S. and United Nations sanctions. It describes the Lazarus Group as created by the North Korean government "as early as 2007" and subordinate to the RGB's 110th Research Center, 3rd Bureau, and lists its targets as government, military, financial, manufacturing, publishing, media, entertainment and international shipping companies.
The Treasury describes the other two as sub-groups. **Bluenoroff**, it says, was formed to earn revenue illegally in response to increased international sanctions, by 2018 had attempted to steal more than $1.1 billion from financial institutions, and had carried out successful operations against more than 16 organizations in 11 countries. **Andariel**, which security firms first noticed around 2015, targets foreign businesses, government agencies, financial infrastructure and the defence industry, and South Korea's government, infrastructure and military in particular, according to the same release, and has tried to steal bank card data by hacking cash machines ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)).
The Treasury describes the other two as sub-groups. **Bluenoroff**, it says, was formed to earn revenue illegally in response to increased international sanctions, by 2018 had attempted to steal more than $1.1 billion from financial institutions, and had carried out successful operations against more than 16 organizations in 11 countries. **Andariel**, which security firms first noticed around 2015, targets foreign businesses, government agencies, financial infrastructure and the defence industry, and South Korea's government, infrastructure and military in particular, according to the same release, and has tried to steal bank card data by hacking cash machines ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)).
North Korea has consistently denied involvement. After the United States attributed WannaCry to it in December 2017, a spokesman for its foreign ministry called the allegations "absurd" and said, ["As we have clearly stated on several occasions, we have nothing to do with cyber-attacks"](https://www.arabnews.com/node/1212316/science-technology) (AFP, 21 December 2017). It rejected the FBI's attribution of the 2026 Binance theft in similar terms (see below).
North Korea has consistently denied involvement. After the United States attributed WannaCry to it in December 2017, a spokesman for its foreign ministry called the allegations "absurd" and said, ["As we have clearly stated on several occasions, we have nothing to do with cyber-attacks"](https://www.arabnews.com/node/1212316/science-technology) (AFP, 21 December 2017). It rejected the FBI's attribution of the 2026 Binance theft in similar terms (see below).
## Major operations attributed to it
## Major operations attributed to it
### Sony Pictures, 2014
### Sony Pictures, 2014
The U.S. Treasury states that the Lazarus Group ["was also directly responsible for the well-known 2014 cyber-attacks of Sony Pictures Entertainment"](https://home.treasury.gov/news/press-releases/sm774). This was the attack that the 2016 private reports set out to trace ([SecurityWeek, 24 February 2016](https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/)).
The U.S. Treasury states that the Lazarus Group ["was also directly responsible for the well-known 2014 cyber-attacks of Sony Pictures Entertainment"](https://home.treasury.gov/news/press-releases/sm774). This was the attack that the 2016 private reports set out to trace ([SecurityWeek, 24 February 2016](https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/)).
### Bangladesh Bank, 2016
### Bangladesh Bank, 2016
In February 2016 attackers took US$81 million from Bangladesh Bank's account at the Federal Reserve Bank of New York, and the money was [wired to banks in the Philippines and Sri Lanka](https://www.benarnews.org/english/news/bengali/Central-Bank-heist-05102016152040.html) (BenarNews, 10 May 2016). The Treasury attributes the theft to Bluenoroff working with the Lazarus Group. It says they used stolen credentials for SWIFT, the interbank messaging network, to send more than 36 large transfer requests totalling $851 million, and that a typographical error alerted staff to the scheme ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)).
In February 2016 attackers took US$81 million from Bangladesh Bank's account at the Federal Reserve Bank of New York, and the money was [wired to banks in the Philippines and Sri Lanka](https://www.benarnews.org/english/news/bengali/Central-Bank-heist-05102016152040.html) (BenarNews, 10 May 2016). The Treasury attributes the theft to Bluenoroff working with the Lazarus Group. It says they used stolen credentials for SWIFT, the interbank messaging network, to send more than 36 large transfer requests totalling $851 million, and that a typographical error alerted staff to the scheme ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)).
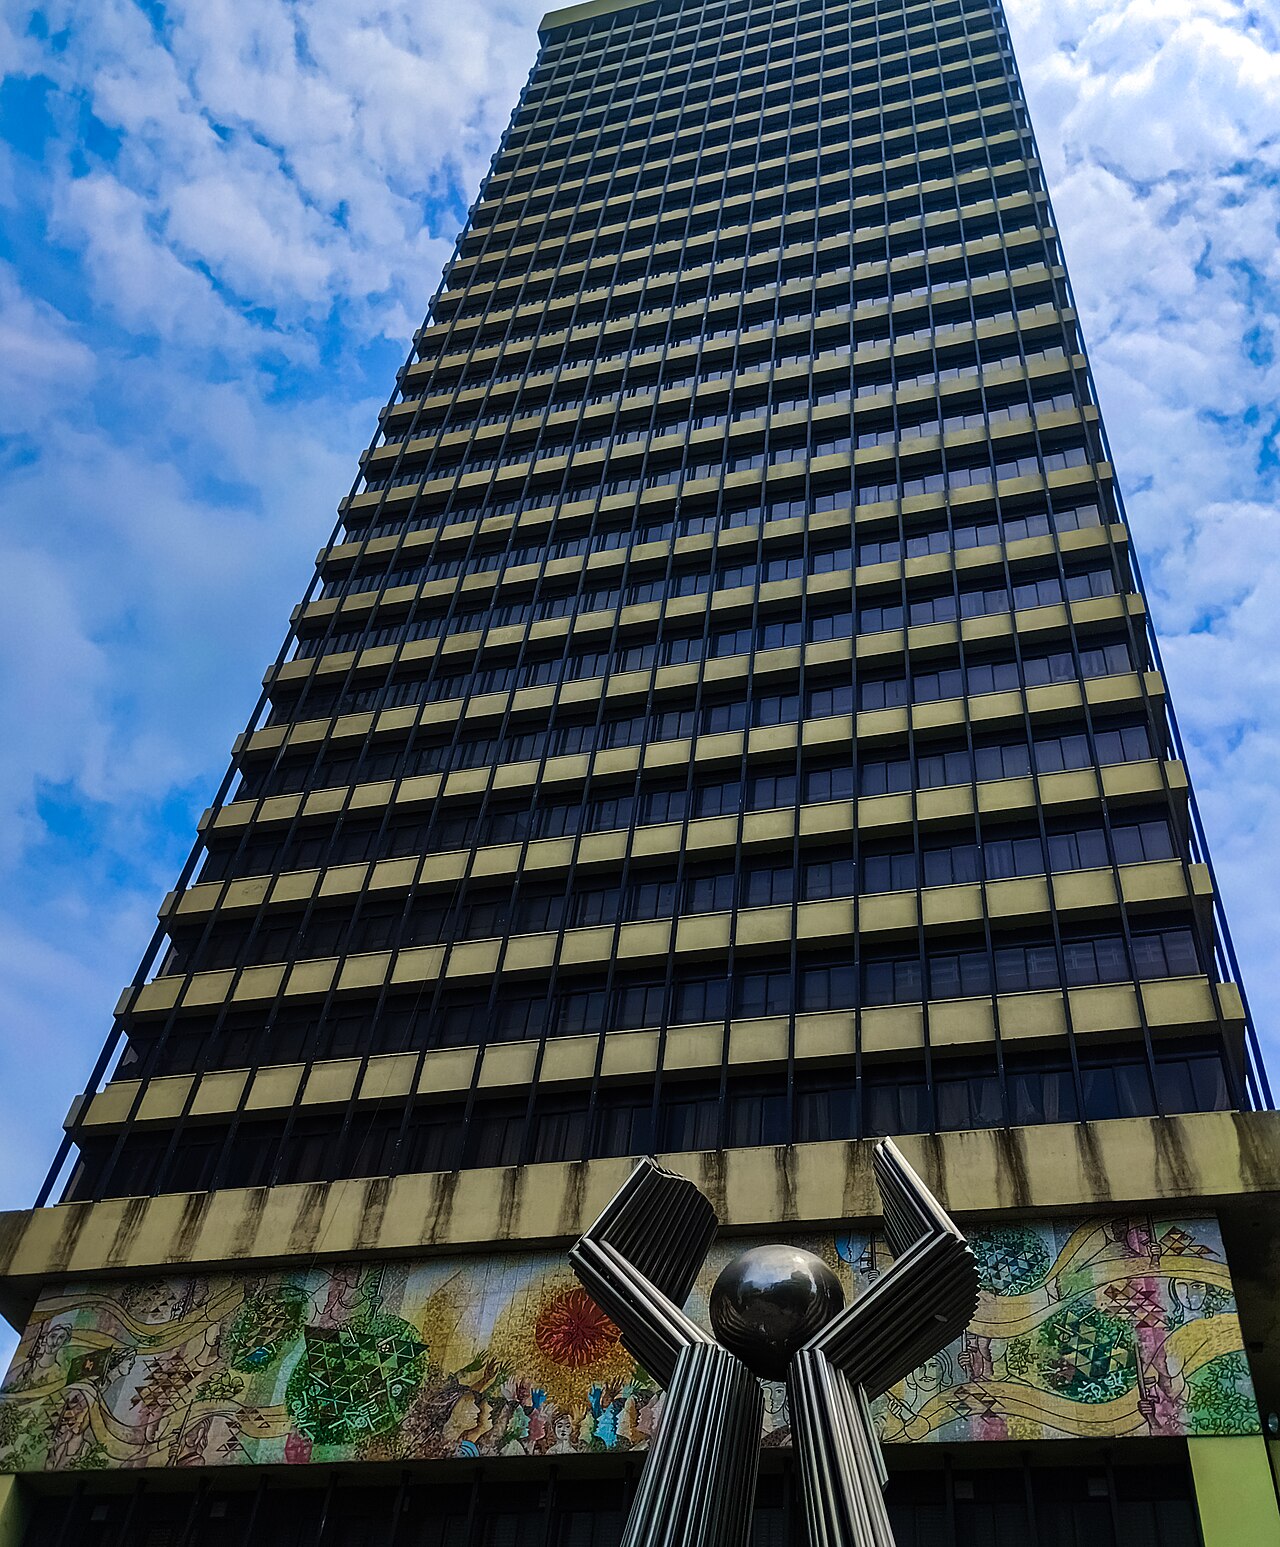

*Via Wikimedia Commons: [Bangladesh Bank Main Building](https://commons.wikimedia.org/wiki/File:Bangladesh_Bank_Main_Building.jpg) by Mrb Rafi, [CC BY-SA 4.0](https://creativecommons.org/licenses/by-sa/4.0).*
*Via Wikimedia Commons: [Bangladesh Bank Main Building](https://commons.wikimedia.org/wiki/File:Bangladesh_Bank_Main_Building.jpg) by Mrb Rafi, [CC BY-SA 4.0](https://creativecommons.org/licenses/by-sa/4.0).*
### WannaCry, 2017
### WannaCry, 2017
WannaCry was ransomware: malicious software that encrypts a computer's files and demands payment to release them. It spread on Friday 12 May 2017 ([National Audit Office, 27 October 2017](https://www.nao.org.uk/reports/investigation-wannacry-cyber-attack-and-the-nhs/)). In December 2017 the United States, Australia, Canada, New Zealand and the United Kingdom publicly attributed it to North Korea, according to the Treasury, which says it affected at least 150 countries and shut down about 300,000 computers ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)). The UK's National Cyber Security Centre assessed that it was ["highly likely that North Korean actors known as the Lazarus Group were behind"](https://www.gov.uk/government/news/foreign-office-minister-condemns-north-korean-actor-for-wannacry-attacks) the campaign (Foreign and Commonwealth Office, 19 December 2017).
WannaCry was ransomware: malicious software that encrypts a computer's files and demands payment to release them. It spread on Friday 12 May 2017 ([National Audit Office, 27 October 2017](https://www.nao.org.uk/reports/investigation-wannacry-cyber-attack-and-the-nhs/)). In December 2017 the United States, Australia, Canada, New Zealand and the United Kingdom publicly attributed it to North Korea, according to the Treasury, which says it affected at least 150 countries and shut down about 300,000 computers ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)). The UK's National Cyber Security Centre assessed that it was ["highly likely that North Korean actors known as the Lazarus Group were behind"](https://www.gov.uk/government/news/foreign-office-minister-condemns-north-korean-actor-for-wannacry-attacks) the campaign (Foreign and Commonwealth Office, 19 December 2017).
The National Health Service in England was among the worst affected. The National Audit Office found that at least 81 of the 236 NHS trusts in England were affected, and that NHS England estimated more than 19,000 appointments were cancelled, though it recorded only 6,912 directly ([NAO, 2017](https://www.nao.org.uk/reports/investigation-wannacry-cyber-attack-and-the-nhs/)). The Treasury puts the eventual cost to the NHS at more than $112 million and calls WannaCry "the biggest known ransomware outbreak in history" ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)).
The National Health Service in England was among the worst affected. The National Audit Office found that at least 81 of the 236 NHS trusts in England were affected, and that NHS England estimated more than 19,000 appointments were cancelled, though it recorded only 6,912 directly ([NAO, 2017](https://www.nao.org.uk/reports/investigation-wannacry-cyber-attack-and-the-nhs/)). The Treasury puts the eventual cost to the NHS at more than $112 million and calls WannaCry "the biggest known ransomware outbreak in history" ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)).
### Cryptocurrency thefts
### Cryptocurrency thefts
The Treasury estimated that the three groups likely stole around $571 million in cryptocurrency from five exchanges in Asia between January 2017 and September 2018 ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)).
The Treasury estimated that the three groups likely stole around $571 million in cryptocurrency from five exchanges in Asia between January 2017 and September 2018 ([U.S. Treasury, 2019](https://home.treasury.gov/news/press-releases/sm774)).
In April 2022 the FBI, the Cybersecurity and Infrastructure Security Agency (CISA) and the Treasury issued a joint advisory on what they called TraderTraitor, a series of malicious cryptocurrency applications. It describes intrusions that begin with large numbers of targeted "spearphishing" messages to staff of cryptocurrency companies, often those working in system administration or in software development and IT operations (DevOps), frequently presented as recruitment offers for well-paid jobs that lead the victim to download the malicious software. The listed targets include exchanges, decentralized finance (DeFi) services, play-to-earn games, trading firms, cryptocurrency venture funds and individuals holding large amounts of cryptocurrency ([CISA advisory AA22-108A, April 2022](https://www.cisa.gov/news-events/cybersecurity-advisories/aa22-108a)).
In April 2022 the FBI, the Cybersecurity and Infrastructure Security Agency (CISA) and the Treasury issued a joint advisory on what they called TraderTraitor, a series of malicious cryptocurrency applications. It describes intrusions that begin with large numbers of targeted "spearphishing" messages to staff of cryptocurrency companies, often those working in system administration or in software development and IT operations (DevOps), frequently presented as recruitment offers for well-paid jobs that lead the victim to download the malicious software. The listed targets include exchanges, decentralized finance (DeFi) services, play-to-earn games, trading firms, cryptocurrency venture funds and individuals holding large amounts of cryptocurrency ([CISA advisory AA22-108A, April 2022](https://www.cisa.gov/news-events/cybersecurity-advisories/aa22-108a)).
On 26 February 2025 the FBI stated that North Korea was responsible for the theft of approximately $1.5 billion in virtual assets from the exchange Bybit on or about 21 February 2025, under the TraderTraitor name. It said the thieves were converting some of the stolen assets to bitcoin and other assets and dispersing them across thousands of addresses on several blockchains, and expected them to be further laundered and eventually converted to ordinary currency ([FBI, 26 February 2025](https://www.ic3.gov/PSA/2025/PSA250226)).
On 26 February 2025 the FBI stated that North Korea was responsible for the theft of approximately $1.5 billion in virtual assets from the exchange Bybit on or about 21 February 2025, under the TraderTraitor name. It said the thieves were converting some of the stolen assets to bitcoin and other assets and dispersing them across thousands of addresses on several blockchains, and expected them to be further laundered and eventually converted to ordinary currency ([FBI, 26 February 2025](https://www.ic3.gov/PSA/2025/PSA250226)).
### Binance, 2026
### Binance, 2026
As of November 2026 this case is still being investigated. On Saturday 31 October 2026 the FBI said North Korea was responsible for the theft of more than $6 billion in virtual assets from the exchange Binance [on or about 29 October 2026](https://www.euronews.com/2026/11/01/fbi-blames-north-korea-for-63-billion-binance-crypto-hack), again naming the activity TraderTraitor, and said it had observed the stolen assets being converted into ether (Euronews, 1 November 2026). Reuters reported on 3 November that North Korea's state news agency KCNA had carried a statement by Kim Yo Jong, a ruling-party official and the sister of leader Kim Jong Un, calling the claim ["absurd rhetoric and nothing new"](https://theprint.in/world/north-korea-says-claims-linking-it-to-binance-heist-are-absurd-rhetoric-kcna-says/3088753/) and "a grave political provocation" (Reuters, 3 November 2026).
As of November 2026 this case is still being investigated. On Saturday 31 October 2026 the FBI said North Korea was responsible for the theft of more than $6 billion in virtual assets from the exchange Binance [on or about 29 October 2026](https://www.euronews.com/2026/11/01/fbi-blames-north-korea-for-63-billion-binance-crypto-hack), again naming the activity TraderTraitor, and said it had observed the stolen assets being converted into ether (Euronews, 1 November 2026). Reuters reported on 3 November that North Korea's state news agency KCNA had carried a statement by Kim Yo Jong, a ruling-party official and the sister of leader Kim Jong Un, calling the claim ["absurd rhetoric and nothing new"](https://theprint.in/world/north-korea-says-claims-linking-it-to-binance-heist-are-absurd-rhetoric-kcna-says/3088753/) and "a grave political provocation" (Reuters, 3 November 2026).
## Methods
## Methods
The sources describe a few recurring methods. One is the use of fake job offers and recruitment to persuade employees to run malicious software, set out in the 2022 TraderTraitor advisory ([CISA](https://www.cisa.gov/news-events/cybersecurity-advisories/aa22-108a)). Another is the use of stolen credentials to send instructions through legitimate financial systems, as in the Bangladesh Bank case ([U.S. Treasury](https://home.treasury.gov/news/press-releases/sm774)). After a theft of cryptocurrency, the FBI has described rapid conversion of stolen tokens and their dispersal across many addresses and blockchains ([FBI, 2025](https://www.ic3.gov/PSA/2025/PSA250226)). The Treasury links the revenue-raising side of this activity to international sanctions on North Korea ([U.S. Treasury](https://home.treasury.gov/news/press-releases/sm774)).
The sources describe a few recurring methods. One is the use of fake job offers and recruitment to persuade employees to run malicious software, set out in the 2022 TraderTraitor advisory ([CISA](https://www.cisa.gov/news-events/cybersecurity-advisories/aa22-108a)). Another is the use of stolen credentials to send instructions through legitimate financial systems, as in the Bangladesh Bank case ([U.S. Treasury](https://home.treasury.gov/news/press-releases/sm774)). After a theft of cryptocurrency, the FBI has described rapid conversion of stolen tokens and their dispersal across many addresses and blockchains ([FBI, 2025](https://www.ic3.gov/PSA/2025/PSA250226)). The Treasury links the revenue-raising side of this activity to international sanctions on North Korea ([U.S. Treasury](https://home.treasury.gov/news/press-releases/sm774)).
## Sources
## Sources
- U.S. Department of the Treasury, "Treasury Sanctions North Korean State-Sponsored Malicious Cyber Groups", press release, 13 September 2019. https://home.treasury.gov/news/press-releases/sm774
- Eduard Kovacs, "Sony Hackers Linked to Many Espionage, Destruction Campaigns", SecurityWeek, 24 February 2016. https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/
- Cybersecurity and Infrastructure Security Agency, FBI and U.S. Treasury, "TraderTraitor: North Korean State-Sponsored APT Targets Blockchain Companies", advisory AA22-108A, 18 April 2022 (revised 20 April 2022). https://www.cisa.gov/news-events/cybersecurity-advisories/aa22-108a
- Federal Bureau of Investigation, "North Korea Responsible for $1.5 Billion Bybit Hack", public service announcement, 26 February 2025. https://www.ic3.gov/PSA/2025/PSA250226
- Foreign and Commonwealth Office (UK), "Foreign Office Minister condemns North Korean actor for WannaCry attacks", 19 December 2017. https://www.gov.uk/government/news/foreign-office-minister-condemns-north-korean-actor-for-wannacry-attacks
- National Audit Office (UK), *Investigation: WannaCry cyber attack and the NHS*, 27 October 2017. https://www.nao.org.uk/reports/investigation-wannacry-cyber-attack-and-the-nhs/
- "Bangladesh Bank, NY Fed and SWIFT Vow to Solve $81 Million Heist", BenarNews, 10 May 2016. https://www.benarnews.org/english/news/bengali/Central-Bank-heist-05102016152040.html
- AFP, "North Korea denies role in WannaCry ransomware attack", via Arab News, 21 December 2017. https://www.arabnews.com/node/1212316/science-technology
- Nathan Rennolds, "FBI blames North Korea for $6.3 billion Binance crypto hack", Euronews, 1 November 2026. https://www.euronews.com/2026/11/01/fbi-blames-north-korea-for-63-billion-binance-crypto-hack
- Reuters, "North Korea says claims linking it to Binance heist are 'absurd rhetoric,' KCNA says", via ThePrint, 3 November 2026. https://theprint.in/world/north-korea-says-claims-linking-it-to-binance-heist-are-absurd-rhetoric-kcna-says/3088753/
- U.S. Department of the Treasury, "Treasury Sanctions North Korean State-Sponsored Malicious Cyber Groups", press release, 13 September 2019. https://home.treasury.gov/news/press-releases/sm774
- Eduard Kovacs, "Sony Hackers Linked to Many Espionage, Destruction Campaigns", SecurityWeek, 24 February 2016. https://www.securityweek.com/sony-hackers-linked-many-espionage-destruction-campaigns/
- Cybersecurity and Infrastructure Security Agency, FBI and U.S. Treasury, "TraderTraitor: North Korean State-Sponsored APT Targets Blockchain Companies", advisory AA22-108A, 18 April 2022 (revised 20 April 2022). https://www.cisa.gov/news-events/cybersecurity-advisories/aa22-108a
- Federal Bureau of Investigation, "North Korea Responsible for $1.5 Billion Bybit Hack", public service announcement, 26 February 2025. https://www.ic3.gov/PSA/2025/PSA250226
- Foreign and Commonwealth Office (UK), "Foreign Office Minister condemns North Korean actor for WannaCry attacks", 19 December 2017. https://www.gov.uk/government/news/foreign-office-minister-condemns-north-korean-actor-for-wannacry-attacks
- National Audit Office (UK), *Investigation: WannaCry cyber attack and the NHS*, 27 October 2017. https://www.nao.org.uk/reports/investigation-wannacry-cyber-attack-and-the-nhs/
- "Bangladesh Bank, NY Fed and SWIFT Vow to Solve $81 Million Heist", BenarNews, 10 May 2016. https://www.benarnews.org/english/news/bengali/Central-Bank-heist-05102016152040.html
- AFP, "North Korea denies role in WannaCry ransomware attack", via Arab News, 21 December 2017. https://www.arabnews.com/node/1212316/science-technology
- Nathan Rennolds, "FBI blames North Korea for $6.3 billion Binance crypto hack", Euronews, 1 November 2026. https://www.euronews.com/2026/11/01/fbi-blames-north-korea-for-63-billion-binance-crypto-hack
- Reuters, "North Korea says claims linking it to Binance heist are 'absurd rhetoric,' KCNA says", via ThePrint, 3 November 2026. https://theprint.in/world/north-korea-says-claims-linking-it-to-binance-heist-are-absurd-rhetoric-kcna-says/3088753/
